In this article
On October 21, 2026, the U.S. National Security Agency (NSA) published an advisory called “Critical Patches Recommended for PHP Vulnerabilities.” The flaws have a nickname, PHP2Shell, and the warning is serious: on a server running an affected version of PHP, an attacker could take control without a password.
That sounds technical, so we’ll explain it the simple way. And if you are an Edilab client, here is the short version first: you are safe. None of the websites, apps or systems we build run on PHP.
What is PHP? The simple version
Imagine a website is a restaurant. The pages you see are the plates of food. Some websites keep every plate ready on a shelf. Others cook each plate fresh in a kitchen every time a visitor asks for one.
PHP is one of the most popular “kitchens” on the internet. It is a programming language that runs on the web server and builds pages on the fly. It has been around for decades, and a huge number of websites use it, including every site built on WordPress, Drupal, Joomla or Magento.
What is PHP2Shell?
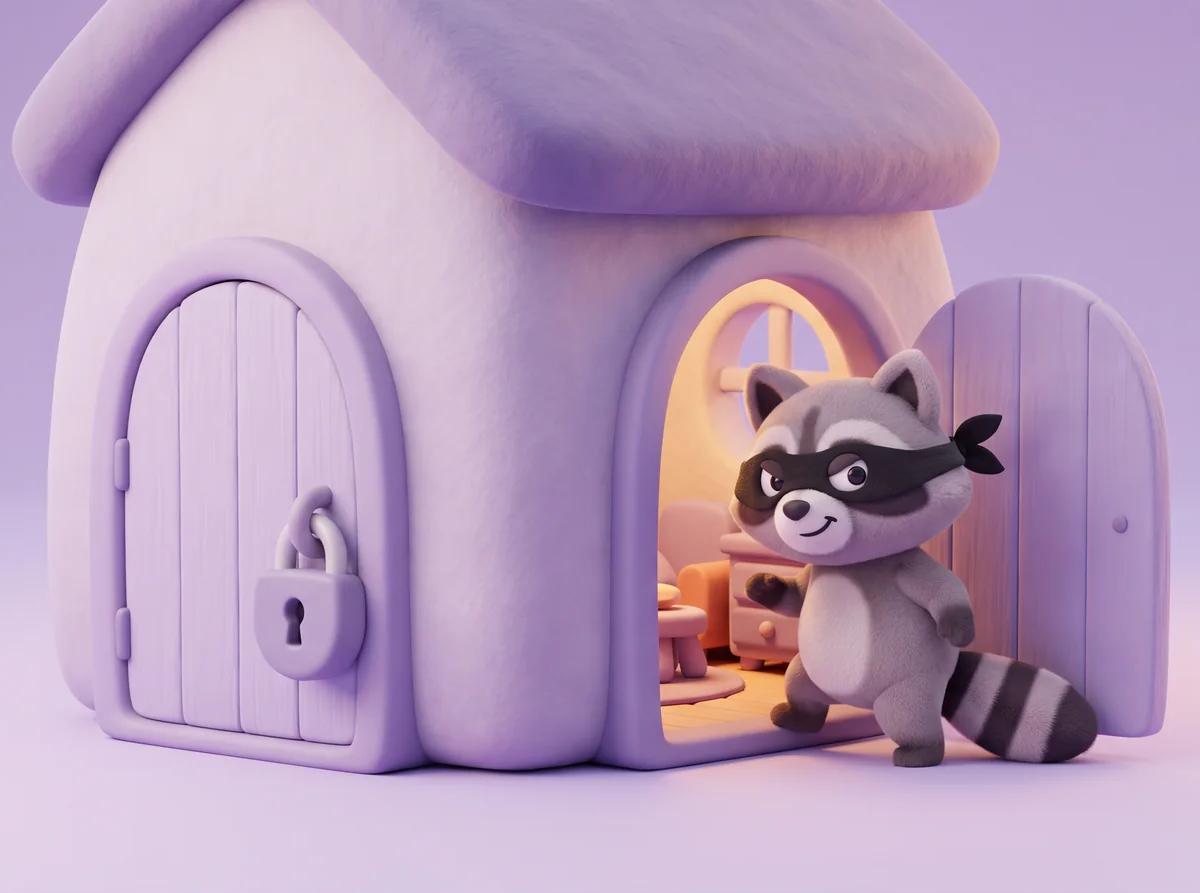
Now imagine your house has a strong lock on the front door, but someone discovers that the back door doesn’t lock at all. It doesn’t matter how good your front door is. Anyone who knows about the back door can walk right in.
PHP2Shell is that back door. According to the NSA:
- The flaws are in PHP itself, not in one particular website or its settings. Servers running affected PHP versions can be attacked.
- An attacker could take control of the web server without any password or prior access.
- From there they could steal sensitive data, break the website, or move deeper into the company’s network.
The NSA expects attackers to start using these flaws, and called the risk serious enough to require immediate patching across U.S. government departments and agencies.
A website that brings in customers.
Fixed-price websites, stores and booking systems — written, designed and built by our studio.
Who is at risk?
Any website or system running on a server with an affected version of PHP. In plain words, check your business if:
- Your website is built on WordPress, Drupal, Joomla or Magento.
- Your site lives on a classic shared hosting plan with cPanel.
- Your page addresses end in .php.
- You use an older custom system, client portal or booking tool built in PHP.
- Your server runs a PHP version that no longer gets updates. Those may not be able to receive the fix at all.
Not sure what your website runs on? That is completely normal. Most business owners don’t know, and that is exactly why it is worth asking today.
What to do right now if your site uses PHP
Here is the NSA’s advice in plain English:
- Update PHP. The PHP team released its fix on Wednesday, October 21, 2026. The details are on the PHP.net security page.
- Ask your host or developer to confirm it is done. Get a clear yes. Other software vendors may release their own patches in the coming weeks, so keep watching for updates.
- Make a list of every website, portal and tool your business uses that runs on PHP, so nothing is forgotten.
- Turn on extra logging, so you would notice if someone tried to get in.
- Replace old PHP versions that can no longer be patched.
- Can’t update yet? Take it offline until it is fixed. A website that is down for a day costs far less than a website that gets taken over.

Why every Edilab client is safe
We don’t build on PHP. Our custom websites, apps and client portals are built with modern JavaScript frameworks, and our business websites run on managed platforms like Wix, where the platform maintains the servers. None of the websites, apps or systems we build use PHP, so PHP2Shell has no back door to open.
We didn’t just assume it. On October 22, the day after the advisory, we checked every live website and app we have built for our clients. None of them run on PHP.
That is not luck. We choose modern tools and managed platforms on purpose, so a security emergency like this one doesn’t turn into your emergency. If you want to know more about how we build, see our websites and custom software.
Quick answers
Has my website been hacked?
Not necessarily. These flaws mean an affected site can be attacked, not that it has been. Update first, then ask your developer to review the server logs.
Does this affect WordPress?
WordPress runs on PHP, so any WordPress site on a server with an affected PHP version needs the PHP update. Ask your host to confirm their PHP version is patched.
I’m an Edilab client. Do I need to do anything?
No. None of the websites, apps or systems we build use PHP.
My website was built by someone else. Can you help?
Yes. Book a free 20-minute call, send us your website address, and we will look at it with you and tell you what to do next.
Leads growth, strategy and client relationships — turning a business owner's vision into high-converting websites, systems and brand experiences.
About the studio →